这篇也收在 aaronlau.me:TLS 1.3 要 OpenSSL 1.1.1
Nginx 学习笔记 (a0) - 开启 HTTP/2, TLS 1.3 和 HSTS
这篇文章写于 2019 年,距今 7 年。文中的做法和默认值可能已经变化,动手前请对照官方文档。
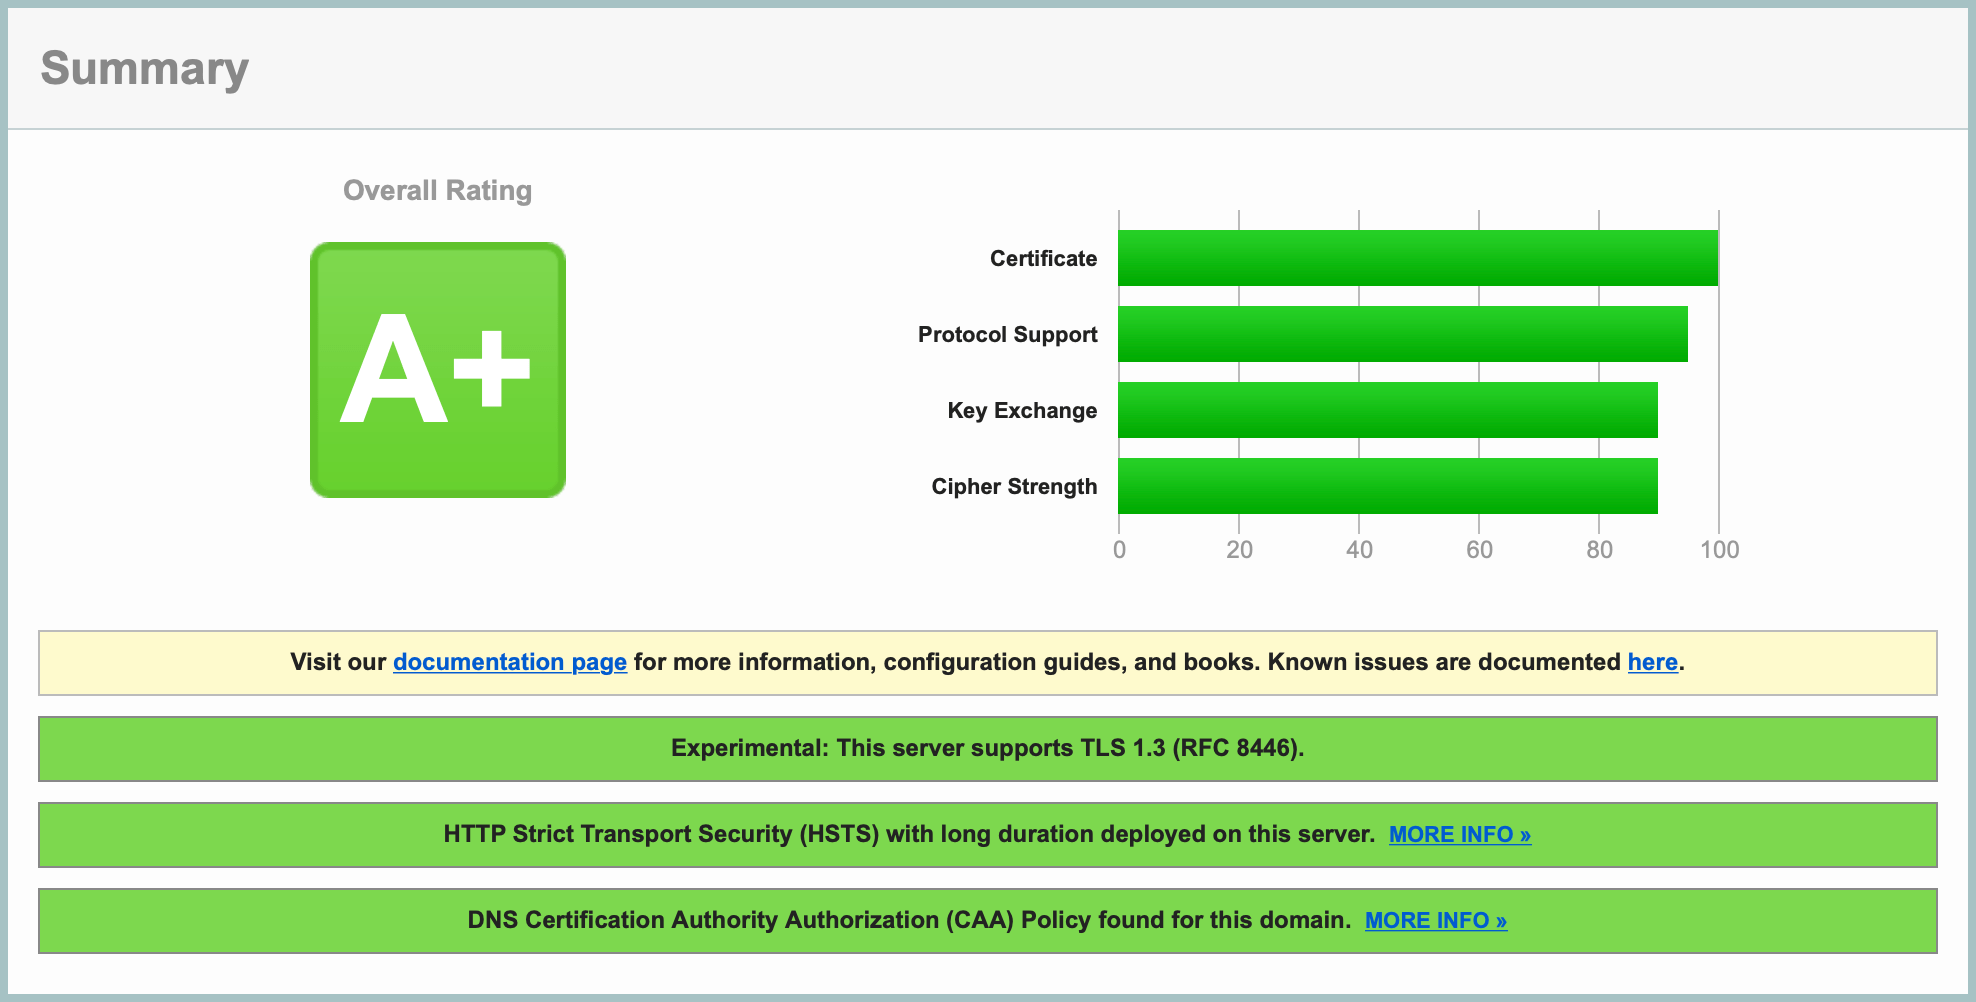
不过瘾?再折腾 HTTP/2 (检测)、TLS 1.3 (检测) 和 HSTS (检测),力求在 SSL Server Test 达到 A+!
安装新版 OpenSSL (新版本见)。要启用 TLS 1.3,起码得 1.1.1 以上才行。
cd /usr/local/src wget https://www.openssl.org/source/openssl-1.1.1d.tar.gz && tar zxf openssl-1.1.1d.tar.gz && cd openssl-1.1.1d
./config --prefix=/usr/local/openssl make && make install
替换掉旧版,尔后以
openssl version判断是否升级完成。mv /usr/bin/openssl /usr/bin/openssl.old mv /usr/include/openssl /usr/include/openssl.old ln -s /usr/local/openssl/bin/openssl /usr/bin/openssl ln -s /usr/local/openssl/include/openssl /usr/include/openssl
echo "/usr/local/openssl/lib/" >> /etc/ld.so.conf ldconfig -v
nginx -V列出现有的参数。追加参数--with-openssl=../openssl-1.1.1d后,重新编译 Nginx。cd /usr/local/src/nginx-1.16.1
./configure
--with-http_ssl_module
--with-http_v2_module
--with-http_sub_module
--with-openssl=../openssl-1.1.1dmake mv /usr/local/nginx/sbin/nginx /usr/local/nginx/sbin/nginx.old cp objs/nginx /usr/local/nginx/sbin/nginx make upgrade
回去编辑 server.conf (至于 Cipher Suites 的部分,不妨参考下 Cloudflare 的配置)。另外提醒 HSTS 是浏览器端直接强制 HTTPS,而非 HTTP 301 重定向至 HTTPS,如不确定后续会否继续使用 HTTPS,请注释掉那行代码。
server { ... listen 443 ssl http2; ssl_protocols TLSv1.3; add_header Strict-Transport-Security 'max-age=63072000; includeSubDomains; preload'; ... }
⚠️ 如果前面使用的 Certbot,要么注释掉 include /etc/letsencrypt/options-ssl-nginx.conf;,要么不用加 ssl_protocols TLSv1.3;。
Aaron Lau这里的文章写于 2010 年代。现在每天的文字在 aaronlau.me,手上在做的是 AI System 6。

这篇在 aaronlau.me 也有存档版本。去那边读
评论